N-central 2026.3 Hotfix 3 – CVE-2026-86206 and CVE-2026-86207

Build Number: 2026.3.1.13   

Last Updated: Sept 5th 2026 

Security Update 

This hotfix includes security fixes for CVE-2026-86206 and CVE-2026-86207 which are high-CVSS-rated vulnerabilities that could allow an unauthorized party to bypass authentication controls and gain full access to the N-central platform.  

The vulnerabilities were responsibly disclosed by a third party through our security disclosure program. At this time, we have no confirmations that these vulnerabilities have been exploited in production environments, but unpatched systems remain at risk. 

Customers running on-premises N-central deployments should upgrade to N-central 2026.3 HF3 immediately to protect their environment. 

Download links:

N-central

N-central CMMC Download (For CMMC Subscribed Accounts) 

Additional Information 

This release supersedes N-central 2026.3 Hotfix 2 (build 2026.3.1.10). For details about the 2026.3 Hotfix 2 release, see 2026.3 HF2 Release Notes. To learn what’s included in the 2026.3 release, see N-central 2026.3 Release Notes.

Hosted N-central – No action required 

If you are on an N-central hosted instance (NCOD), patches have already been applied to your environment. You do not need to do anything at this time. 

N-central (self-hosted) – How do I upgrade to the hotfix? 

Download and upgrade to 2026.3.1.13 using the instructions provided below and, on the N-able support portal. If you need assistance with the upgrade process, please contact our support team at https://me.n-able.com/s/ 

Upgrade Documentation: https://documentation.n-able.com/N-central/userguide/Content/ReleaseDocs/Install_Config/InstallConfig_Upgrade.htm 

Upgrading from legacy versions: https://documentation.n-able.com/N-central/userguide/Content/ReleaseDocs/Release_Notes/upgrade_path.htm 

Supported Upgrade Paths 

  • Upgrade directly to 2026.3.1.13 from:  
  • 2025.4 
  • 2026.1 
  • 2026.2 
  • 2026.3 
  • 2026.3.1 (Hotfix 1) 
  • 2026.3.1 (Hotfix 2) 

If you are on an older version, we recommend going to any of the builds above, then upgrading to this hotfix version ASAP. If you are unsure of what to do, you can contact support directly. 

Do I need to update my agents too? 

While the hotfix itself does not require agents to be upgraded to protect you from CVE-2026-86206 and CVE-2026-86207. As a best practice we always recommend that you upgrade agents to the latest available version. 

For More Information: 

Support: https://me.n-able.com/s/ 

Uptime Page: https://uptime.n-able.com/ 

Posted in N-central | Comments Off on N-central 2026.3 Hotfix 3 – CVE-2026-86206 and CVE-2026-86207

New in Adlumin: Enhanced M365 Session Hijacking Detection Now Live

We’re excited to announce AI-powered anomaly detection enhancements designed to catch the sophisticated attacks that traditional rules-based techniques miss.

The Challenge We’ve Solved

Improbable travel detection is effective at catching attackers who move between distant locations at unrealistic speeds. However, cybercriminals increasingly use VPNs and anonymizers to hide their true locations. These zero-velocity hijacks – where the attacker appears to be in the same location as the legitimate user – have remained difficult for traditional detection methods to identify.

Continue reading
Posted in Adlumin | Comments Off on New in Adlumin: Enhanced M365 Session Hijacking Detection Now Live

Easier Access to Ecoverse in N-sight 

The fastest path to N-sight’s newest capabilities now starts at the top of the navigation. 

Overview 

The newest capabilities in N-sight RMM™ now live under the Ecoverse navigation area, making them easier to discover and access. By putting them in a predictable location, the tools your technicians use to monitor environments, remediate endpoint risk, and apply AI to daily work are always one click away. 

New Ecoverse capabilities arrive regularly, and a dedicated menu means your team sees them the day they land rather than months later. Everything you do today still works the same way. What changes is how fast the latest capabilities reach the people who benefit from them. 

Continue reading
Posted in N-sight | Comments Off on Easier Access to Ecoverse in N-sight 

Improving File Reputation Accuracy to Reduce False Positive Detections

Product: SentinelOne Endpoint Detection & Response

We’ve updated how SentinelOne evaluates file and process reputation across N-able managed environments to reduce false positive detections — alerts triggered by legitimate software rather than actual threats.

This change refines detection logic for specific, verified behavior so trusted activity isn’t flagged incorrectly, without weakening detection of genuine threats. No action is required on your part; the update has been applied at the policy level.

For details on one of the issues addressed by this update, see our KB article.

Questions? Contact Support and reference this post.

Posted in EDR, N-central, N-sight | Comments Off on Improving File Reputation Accuracy to Reduce False Positive Detections

Detecting Anomalous Process Execution to Expose Living off the Land Attacks (Release Date: September 1)

Anomalous Process Execution Activity identifies processes whose behaviour differs significantly from what is baseline for an environment, then enriches the alert with the domains, network activity, reputation data, and AI command line analysis an analyst needs to reach a verdict quickly and confidently.

Why Process Behaviour Matters for Security

Process telemetry is one of the richest sources of attacker evidence available, and one of the hardest to use well:

  • Legitimate binaries are routinely abused to run malicious payloads
  • Command lines are frequently obfuscated, encoded, or chained
  • Static allow lists and blocklists cannot keep pace with living off the land techniques
  • The same process can be entirely normal on one host and highly suspicious on another
Continue reading
Posted in Adlumin | Comments Off on Detecting Anomalous Process Execution to Expose Living off the Land Attacks (Release Date: September 1)

Expanded AI Service Detection Coverage and Improved Accuracy

N-central and N-sight now detect fourteen additional AI services in use across managed endpoints, alongside accuracy improvements to previously supported detections. Available now in Assets View for both N-central and N-sight.

Continue reading
Posted in N-sight | Tagged , | Comments Off on Expanded AI Service Detection Coverage and Improved Accuracy

Endpoint Remediation: What’s New

Following the recent launch of our Endpoint Remediation area — announced in AI-Accelerated Vulnerability and Patch Management – Public Preview — we’re pleased to share the next round of improvements, shaped by your feedback and our roadmap.


Advanced reboot options, now on Windows and Mac

Interactive end-user reboot prompts are now available across Windows and macOS assets. After a vulnerability remediation or patch installation, you can prompt the end user to reboot rather than forcing it, reducing disruption and avoiding unexpected interruptions while keeping users in control of their own machine.

You can also customise the reboot message shown to users and set a limit on how many times they can defer, giving you the flexibility to deliver a better user experience without losing control of your compliance window.

Saved views for Patch Management

The saved view capabilities you already use in the Assets view are now available in Patch Management. Build and save your own versions of these screens to match the way you actually work. Saved views are coming to Vulnerability Management shortly.


Vulnerability Management view updates and new export options


As customers resolve a rapidly growing volume of detected vulnerabilities, a consistent piece of feedback has been that resolved items linger in the UI longer than they’re useful. Resolved vulnerabilities now remain visible for 30 days, keeping the view focused on what still needs attention. To make sure nothing is lost, we’ve expanded the export options with selectable date ranges, so you can pull historical resolved data whenever you need it for reporting or audit.

Export up to 10’000 rows in pending and failed patch views:

Export limits in the Pending and Failed patch tabs have been raised to 10,000 rows, bringing them in line with the Completed patches tab.


Performance Improvements

We’ve been rolling out a series of performance improvements over recent weeks and that work continues. The sharp increase in detected vulnerabilities across managed assets put real pressure on load and query times, and these changes are aimed squarely at keeping the experience fast at scale. We expect more performance improvements to go live over the next few weeks

Posted in N-central, N-sight | Comments Off on Endpoint Remediation: What’s New

N-central Mobile: A New, Modern Mobile Experience

We previously retired the legacy N-central Mobile app following the identification of security vulnerabilities. Rather than reinstating the existing application, we made the decision to build a new N-central Mobile app from the ground up on a modern, more secure foundation, available for both iOS and Android.

Important: The new N-central Mobile app requires N-central 2026.4 or later. The app cannot be used to connect to N-central servers running earlier versions.

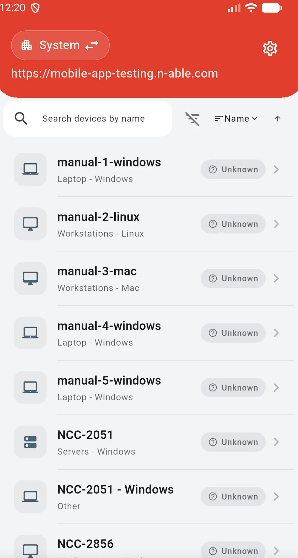
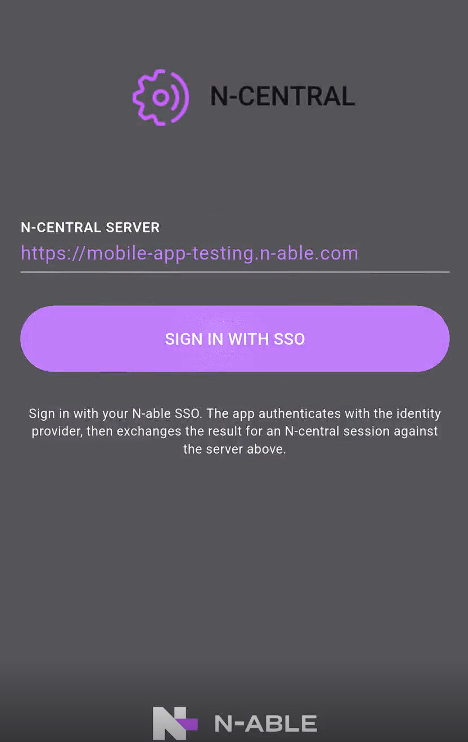
After upgrading to N-central 2026.4, users can take advantage of the new N-central Mobile app on iOS and Android, including N-able Login (SSO) and Take Control functionality.

Here are the links to the applications:

Android: N-central Mobile – Apps on Google Play

iOS: https://apps.apple.com/gb/app/n-central-mobile/id421890006

For this first release, we have intentionally focused the experience on Take Control, one of the most frequently used capabilities in the previous mobile app. This enables technicians to quickly access and remotely support managed devices while on the go, while giving us a strong foundation on which to expand the mobile experience.

With the new N-central Mobile app, you can:

  • Select a customer or site and quickly navigate to its devices.
  • Search and filter the device list to find the device you need.
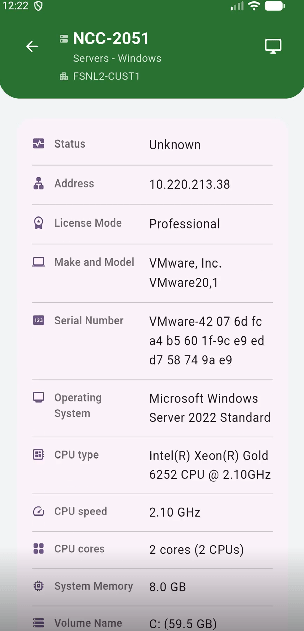
  • View key device details at a glance.
  • Launch Take Control remote sessions directly from your mobile device.
  • Use the app on both iOS and Android devices.
  • Benefit from a modernized foundation designed for improved security, performance, and stability.

What’s Next

This release is the starting point for the new N-central Mobile experience. We are beginning with Take Control and the supporting workflows needed to find and connect to devices quickly.

Over time, we plan to incrementally introduce additional mobile capabilities, informed by partner needs and usage, while continuing to build on the app’s modern foundation.

Sign in with your existing N-central account to get started:

  • Users can authenticate using N-able Login, including MFA and N-able Login. The Mobile App also supports N-able Login with Entra ID. Note: The app differentiates between local login and SSO login for a streamlined login process.

How Login Works:

If Local Login:

  • The app prompts for a password and MFA, then grants access to the product.

If SSO Login:

  • Base N-able Login: The user is forwarded to the N-able Login flow, where they enter their username, password, and MFA (if applicable).
  • N-able Login with a Third-Party IDP: The user is redirected to the third-party provider, follows the external authentication process, and is granted access.

Posted in N-central | Comments Off on N-central Mobile: A New, Modern Mobile Experience

MSP Manager: Mobile – Modernized for iOS

What’s Changed:

The MSP Manager Mobile app has been rebuilt on a modern iOS foundation, providing improved performance and stability while maintaining the workflows technicians use to manage their work from anywhere.

With the updated MSP Manager Mobile app, you can:

  • Manage tickets, customers, contacts, and on-site work from one mobile app
  • Sign in securely using SSO, PIN, or biometrics
  • Track time while on the go
  • Add notes and attachments directly from your mobile device
  • Benefit from performance and stability improvements delivered through the app’s modernized iOS foundation

The rebuild maintains the core MSP Manager workflows technicians already know while providing a more modern and reliable foundation for future mobile improvements.

Getting started:

Log in with your existing MSP Manager account to get started.

Posted in MSP Manager | Comments Off on MSP Manager: Mobile – Modernized for iOS

What’s New in Cove 26.8 – HaloPSA Auto Customer Mapping

In Cove 26.8, we’ve introduced automatic customer mapping for our integration with HaloPSA to reduce the manual effort required to connect Cove customers with their corresponding HaloPSA customers.

This release also delivers continuity improvements designed to strengthen recovery flexibility, reliability, and security.

Continue reading
Posted in Cove Data Protection, Cove Data Protection release notes | Tagged , | Comments Off on What’s New in Cove 26.8 – HaloPSA Auto Customer Mapping