Q2 delivered decisive progress on three fronts: expanding threat detection into blind spots, accelerating incident investigation, and removing operational friction for partners. The quarter reflects a shift toward platform-level capabilities that help security teams detect what matters, investigate faster with confidence, and respond at scale.
Recent releases deliver a range of updates to the Assets View and Asset Details panel in N-central and N-sight – improving how asset data is filtered, displayed, and acted on, alongside a number of usability and design refinements.
Filter by tags directly within the Assets View
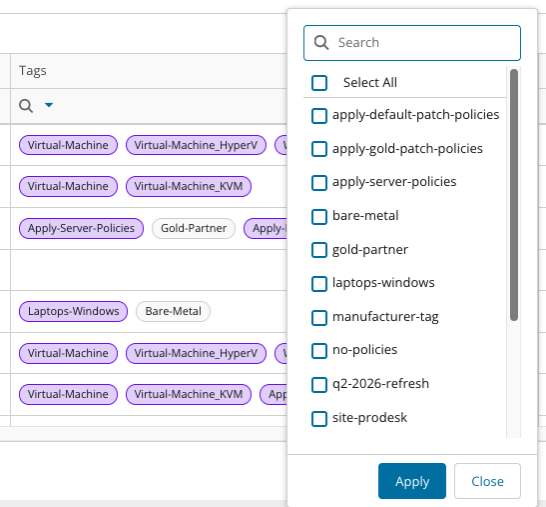
You can now filter assets from within the Assets View using an aggregated filter on the Tags column.
Previously, filtering by tag required remembering and manually typing specific tag names, which didn’t scale for organizations managing hundreds of tags.
The new filter presents all tags currently assigned to assets as a selectable list, so you can quickly find a cohort of assets without needing to recall exact names.
Multiple tags can be selected to broaden the result set.
Assets with no tags will not appear as a filter option.
Apple released macOS Tahoe 26.6 on July 27, 2026. Since then, MSPs have reported that SentinelOne’s Static AI engine is flagging legitimate macOS system processes — including mds, SystemUIServer, loginwindow, and the App Store — as malware on machines running the new build, causing system instability on affected endpoints.
SentinelOne has confirmed the issue and is working on a multi-stage fix, including a global exclusion of the affected hashes, a Live Security Update, and a permanent fix in an upcoming agent release.
If you manage Macs with SentinelOne: hold off on deploying macOS Tahoe 26.6 until this is resolved. If devices have already updated, see the KB article for the current recommended mitigation.
Updated on 6th Aug : This issue has been addressed in the latest macOS agent, i.e., (26.1 SP1) 26.1.3.8805.
Posted inEDR, N-central, N-sight|Comments Off on Known Issue: macOS Tahoe 26.6 Triggers SentinelOne False Positives
We are pleased to announce a major expansion of our vulnerability and patch management capabilities across both N-central and N-sight is currently in the process of being rolled out. The rollout will be completed over the next few days.
Vulnerability management now delivers a closed-loop workflow, enabling technicians to identify, prioritize, remediate, and verify vulnerabilities in one place. The release also expands third-party application patching to support hundreds of additional applications and introduces N-zo Patch Expert, joining the Vulnerability Expert to provide AI-guided recommendations for both vulnerability and patch management decisions.
Together, these enhancements help IT teams find and fix risks faster, reducing manual effort and shrinking exposure windows from days to minutes.
What’s New
Third-Party Application Patching — Windows, macOS, and Linux
N-central and N-sight now include a new, unified third-party application patching engine covering Windows, macOS, and Linux devices. The new patch engine operates alongside our existing Patch Management capabilities, providing an additional option for managing third-party application updates while preserving current patching workflows. Available through both the Patch Management and Vulnerability Management views, it gives technicians greater flexibility in how they identify, prioritize, and remediate third-party software vulnerabilities and updates.
Key capabilities:
Detection and deployment of third-party application updates across all three major operating systems
A single patching engine and workflow experience regardless of platform
Available directly from the Patch Management view for scheduled and on-demand deployments
Available from the Vulnerability Management view as a remediation action, enabling technicians to patch a vulnerable application without leaving the vulnerability workflow
The breadth of coverage matters. With over 550 applications managed from day one, spanning productivity tools, browsers, runtimes, development tools, and more, IT Teams can close the majority of third-party exposure across their estate without stitching together separate tooling for each operating system.
Vulnerability Remediation — Closing the Loop
Historically, vulnerability detection and patch deployment have lived in separate tools, with manual handoffs and context-switching in between. This release closes that gap: third-party patching is now the first remediation action built natively into Vulnerability Management, completing the remediate step in the closed-loop workflow, identify, prioritize, remediate, and verify. Technicians can now move from a vulnerability finding directly to a patch deployment without leaving the workflow.
Additional remediation actions are already in development for future releases, including:
Uninstall application: remove a vulnerable or end-of-life application directly from the vulnerability view
Accept risk: formally document a known risk when remediation isn’t immediately appropriate, supporting audit and compliance needs
N-zo Experts: Vulnerability and Patch Intelligence, Together
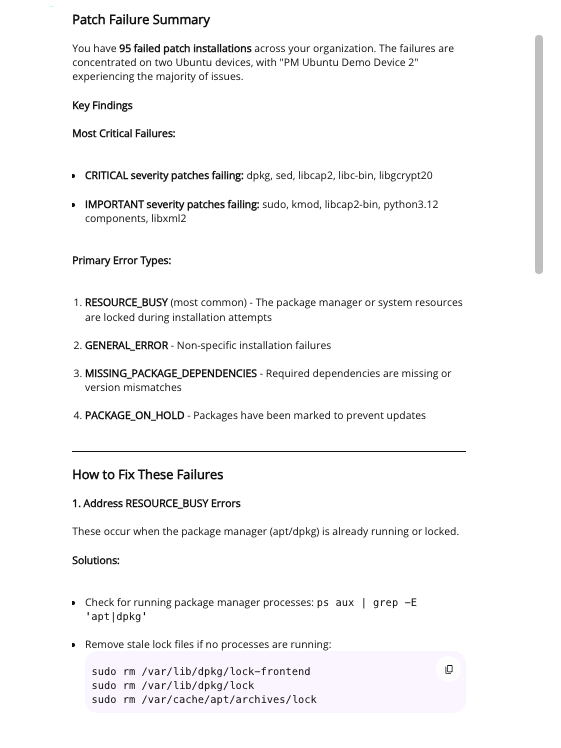
This release adds the N-zo Patch Expert, joining the Vulnerability Expert to bring both vulnerability and patch expertise together inside the product. Together, they give technicians contextual guidance as they work, removing the guesswork over whether a CVE warrants urgent action or which patches to prioritize this cycle. N-zo surfaces that expertise inline, helping IT teams make faster, better-informed decisions.
This is especially valuable for IT teams managing diverse estates across multiple sites, where the volume and variety of vulnerabilities and patches can make consistent, risk-based prioritization difficult to maintain at scale.
Security Insights Dashboard
Introduced as part of our new Endpoint Remediation area, the Security Insights Dashboard provides a consolidated, at-a-glance view of your security and patching posture across managed devices.
Rather than switching between separate patch and vulnerability views to understand exposure, technicians now have a single dashboard that surfaces the information that matters most — and gives them direct paths to act on it.
Each widget is actionable. Technicians can move directly from a dashboard insight to the relevant asset or patch view to investigate and remediate without losing context.
This first version of the Security Insights Dashboard is focused primarily on metadata — giving technicians immediate visibility into severity distribution, CVE details, exploitability context, and patch deployment metrics across the estate. A small number of device-level widgets are also included, with Reboot Status providing a view of assets pending restart following patch deployment.
Future enhancements will go significantly deeper. Planned additions include richer asset health indicators, engine health visibility to surface issues with the patching and vulnerability detection pipeline itself, and support for custom and saved views — allowing technicians to tailor the dashboard to their own workflows and the specific needs of individual customers.
We are introducing Patch Policies, bringing policy-driven automation to the patching workflow and giving technicians greater control over when and how patches are deployed across managed devices.
Availability at launch:
Linux — Patch Policies are now generally available for Linux devices, enabling automated patch scheduling, approval workflows, and deployment rules across Linux estates
macOS — Patch Policies are available in early access preview for macOS, allowing technicians to begin building and testing policy-driven workflows for Apple devices ahead of wider availability
Windows — Patch Policies for Windows devices are coming soon, completing cross-platform policy coverage within the unified patching experience. We have a lot of features being added in here including Patch Tuesday offset scheduling, approval delays, granular options, OS controls and more
Patch Policies allow IT Teams to move away from ad hoc, manual patch decisions and toward a consistent, repeatable approach to patch management, reducing the operational overhead of keeping estates current while maintaining the control needed to manage risk appropriately.
As availability expands across platforms, Patch Policies will become the foundation for scalable, automated patching across the entire managed estate.
Why This Matters for You
Patch management and vulnerability management have traditionally been treated as separate practices. In reality, they are two sides of the same problem: understanding what is exposed across your managed estate and ensuring those exposures are addressed before they are exploited.
This release accelerates that workflow at every stage:
Broader coverage — third-party application patching across Windows, macOS, and Linux means fewer gaps in coverage and fewer tools required to close them
Faster remediation — acting on a vulnerability from within the vulnerability view removes friction and reduces time-to-remediation
Faster identification — the Security Insights Dashboard surfaces the highest-priority risks across all managed devices without manual correlation
AI-assisted decision-making — N-zo expertise means technicians don’t have to carry the full cognitive load of risk prioritisation alone
Greater automation — Patch Policies enable consistent, scalable patch management without relying on manual intervention for every deployment cycle
Uninstall application — remove vulnerable or end-of-life software as a remediation action directly from the vulnerability view
Accept risk — formally document accepted risks for audit and compliance purposes
Patch Policies for Windows — completing cross-platform policy coverage alongside the existing Linux GA and macOS early preview
Windows OS patching in the unified experience — bringing Windows operating system updates into the same modern, cross-platform patching workflow
How to Get Started
Before diving in, there are a few prerequisites to be aware of if you are on N-central.
For the full experience — including the Security Insights Dashboard and the updated left-hand navigation under Endpoint Remediation — you will need to be running N-central v26.2 or later. Customers on earlier versions may still have access to Windows third-party application patching and the vulnerability remediation journey, but will not see the updated navigation or the Security Insights Dashboard and will show within the Linux and Apple patches link.
If you are on N-sight you should be good to go, you should see the new features available from the left hand navigation menus as long as your user permissions are set to allow access to those views.
Posted inN-central, N-sight|Comments Off on AI-Accelerated Vulnerability and Patch Management – Public Preview
We’re introducing significant improvements to Automation Manager, making it easier to build, maintain, and modernize automation policies.
This release adds support for PowerShell 7 through a new automation object, while also delivering a much improved script editing experience for Automation Manager users.
Availability
These Automation Manager improvements are available across N-able platforms:
N-central 26.4 — These features will also be included when N-central 26.4 is released.
PowerShell 7 Support for Automation Policies
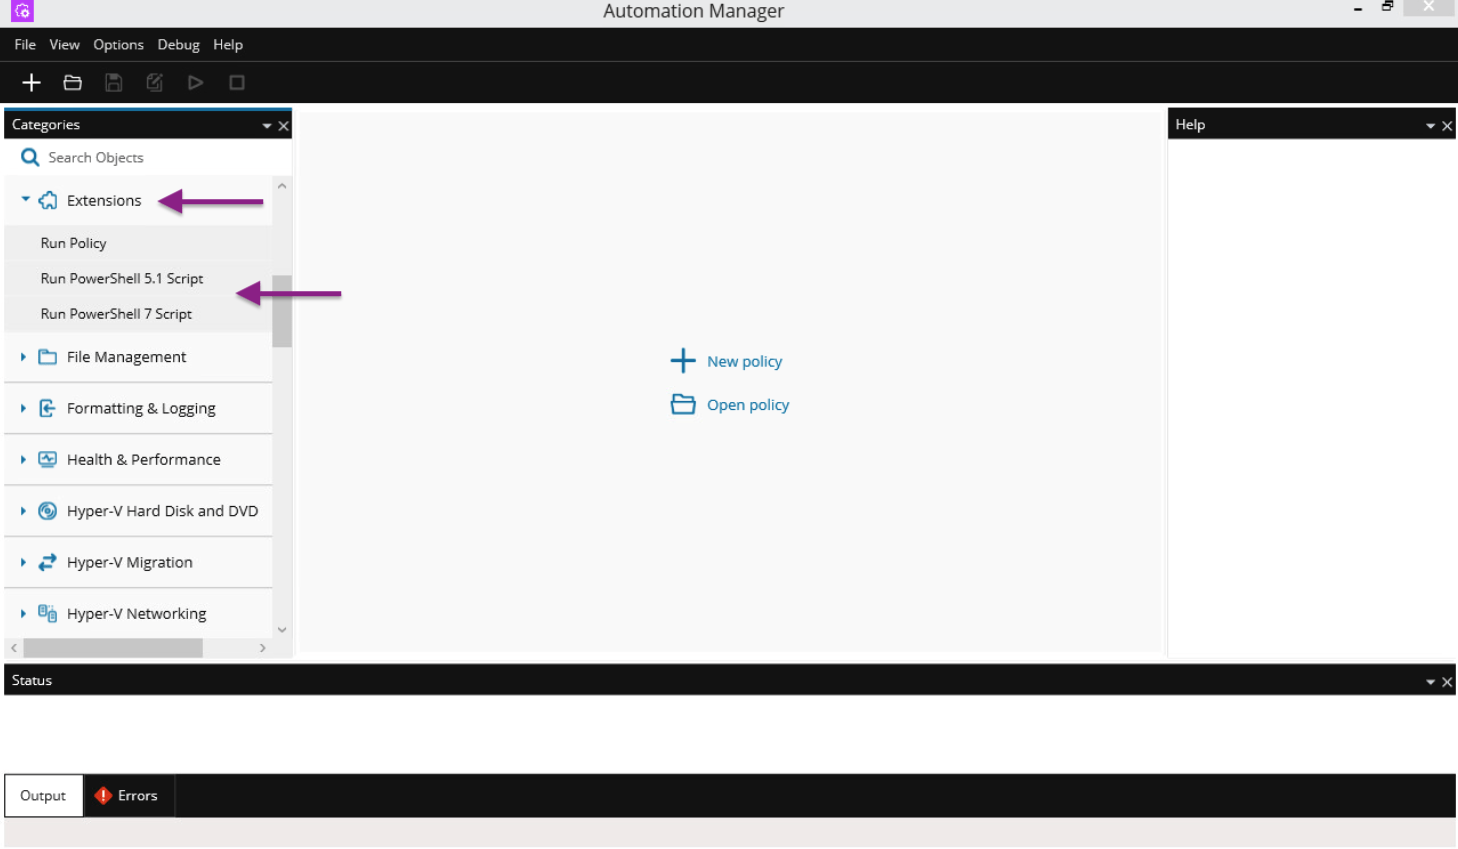
Automation Manager now includes a new Run PowerShell 7 Script object, allowing automation policies to execute scripts using PowerShell 7.
This gives partners access to a more modern PowerShell runtime for new automation scenarios, while preserving compatibility with existing automation policies.
Posted inAutomation Manager, N-central, N-sight|Comments Off on Automation Manager Release – PowerShell 7 Support and Improved Script Editing Experience
Since the Public Preview launch, momentum hasn’t slowed. Driven by partner feedback, Empower conversations, and what we’re seeing in real-world use, we’ve expanded what N-zo can see, what it can answer, and how quickly it gets you there. The headline addition is Patch Expert, but there’s a lot more landing alongside it — faster performance, bigger data sets, and smarter, time-aware prompts. Here’s what’s new, and a look at what’s coming next.
N-zo Assist is a new AI-powered support experience now available in N-ableMe. It lets you ask product questions in plain language, get pointed straight to the right knowledge base article or documentation, and still reach a live support representative or open a ticket whenever you need one. Public preview begins Monday, July 20, 2026.
What is N-zo Assist?
N-zo Assist is an AI chat experience built into N-ableMe that replaces the previous Nash Support Chat. Instead of searching through articles on your own, you can describe what you are trying to do and N-zo Assist finds the relevant knowledge base content, and product documentation for you.
It comes with a refreshed chat icon and look, and it removes friction points like pre-chat forms, so getting started takes one click instead of several.
A new version of the Patch Management Engine is being made available to N-central and N-sight. This release focuses on improving patching reliability, scan accuracy, installer compatibility, and troubleshooting capabilities across supported environments. Customers can benefit from improved diagnostics, more accurate application detection, and enhancements to the handling of Windows Update and reboot scenarios.
What’s New
Improved Feature Update Installation Logging: Enhanced logging has been added around Windows Feature Update installations. By removing redundant log entries and improving diagnostic output, administrators can more easily identify and troubleshoot Feature Update deployment issues. (PMCM-9754)
Improved Offline Scan Detection and WUA Error Handling: PME now includes improved separation between online and offline scan data providers. Additionally, Windows Update Agent (WUA) handling has been refined to better distinguish genuine scan failures from incomplete search warnings and informational messages. This reduces false reporting of scan failures and improves overall scan reliability. (PMCM-11564)
Improved Reboot Handling During Patch Installation (specific for N-sight): PME now better handles scenarios where a patch is not yet detected in the Windows registry but Windows Update Agent reports a successful installation before a required reboot has occurred. This enhancement prevents devices from being incorrectly reported as having failed patch installations when the installation is awaiting completion through a reboot. (PMCM-11757)
Foxit PDF Reader Multi-Language Installer Support: Added support for the latest Foxit PDF Reader multi-language installers, improving compatibility with newer installer packages and ensuring continued support for current Foxit deployment methods. (PMCM-11785)
Improved Google Drive Application Detection: PME no longer detects the Google Drive Native application bundled with Google Chrome as a standalone Google Drive installation. This improves application detection accuracy and helps prevent unnecessary patch evaluations. (PMCM-11819)
Improved Pre-Download Maintenance Window Management: PME now includes an optional feature to stop in-progress patch downloads when a pre-download maintenance window closes. Previously, downloads that started within a window would continue running beyond its end time, which could cause unintended bandwidth consumption — particularly at remote sites with limited connectivity. This feature is disabled by default. (PMCM-11587)
SentinelOne is migrating Singularity Marketplace services to a new environment. As part of this move, the outbound (egress) IP addresses used by Marketplace integrations to connect to third-party tools are changing.
If you have firewall rules, IP allowlists, or other IP-based access controls on any tools connected via Marketplace integrations, please update them with the new region-specific AWS IP addresses to avoid disruption.
Do not remove any existing IP addresses at this time.
N-able considers various features and functionality prior to any final generally available release. As such, comments given in this forum are not (nor should they be interpreted to be) a commitment from N-able that it will deliver any specific feature or, if it delivers such feature, any time frame when that feature will be delivered. N-able is always trying to improve and enhance its products. All discussions herein are based upon product team current interests, and product team plans and priorities can change at any time.





You must be logged in to post a comment.